Latest research update
CClosure dispatch. The README now records the writable CClosure +0x20 field as an arbitrary function-dispatch primitive. Probe 56c directly demonstrates four redirects between existing Lua C functions and their expected return values. This is a confirmed userland capability; it does not establish kernel access or a complete kernel exploit chain. Read the probe log · Finding 82.
KASLR status. The Phase 14 summary reports 17 techniques tested, with every tested path blocked or unsuccessful on 14.10. The README documents the results, including AF_ROUTE sanitization, process-only VM-map results, and blocked or lethal syscall paths. This is the current KASLR wall, not proof that no future technique can work. Read the current status.
Selector 624. Probe 52b reports a stable +5 return delta per mmap. A separate follow-up saw 0xD31 six times, but does not independently establish native dispatch or the selector’s meaning. Follow-up evidence and limits.
13.60 offline analysis. A Ghidra review traces the retained +0x1c4 field through specific write-lock paths in a 13.60-labeled dataset. Acquisition authenticity remains unresolved, so this is not 14.10 kernel evidence. Analysis and limitations.
14.10 status: The README reports no validated kernel vulnerability, kernel read/write, or complete kernel exploit. Hypervisor bypass is also not demonstrated. The audited milestone estimate is 30/100; it is a subjective rubric score, not a probability or percent of work complete.

The findings, probe logs, and analysis reports are linked above; each result is limited to its recorded scope.
Current work on 14.10
Phase 14 completed the scoped Sony syscall survey. The current repository describes 14.10 as a KASLR wall: its tested address-discovery paths did not yield kernel access, while several strong userland primitives are confirmed.
| Userland | CClosure +0x20 dispatch, heap R/W, tested syscall invocation, and a 317-region process map are documented |
| KASLR | 17 techniques tested; all tested paths blocked or unsuccessful |
| Kernel vulnerability | Not demonstrated on 14.10 |
| Kernel read/write | Not demonstrated on 14.10 |
| Complete exploit / hypervisor | Not demonstrated on 14.10 |
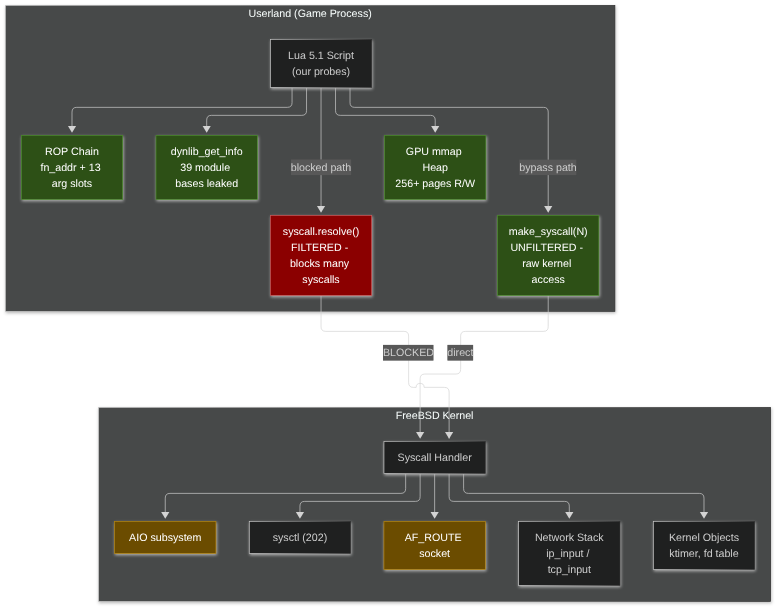
Current constraints
- W^X and execute-only memory limit process-level code execution.
- The confirmed CClosure redirect is a userland primitive; kernel read/write is still unproven.
- The tested KASLR routes have not disclosed a kernel address on 14.10.
- 13.60-labeled static artifacts do not prove behavior or exploitability on 14.10.
Each result is scoped to its recorded experiment. The findings and raw results distinguish observations from interpretations and open questions.
For individual experiments, start with PROBE_INDEX.md. For the sequence of work, read the changelog.
Contributing
Research findings and code analysis are welcome. Include the firmware version, the relevant experiment, and the output behind the finding.
Read CONTRIBUTING.md before opening a pull request. Questions and corrections can go in GitHub issues.
Funding goal: $250 CAD for Claude Max 20x; $3.28 raised at the latest README update. Contribute via PayPal.